
Security
WAAP, API security, bot control, and rate limits
Decide
Application security, request-path control, cache and delivery policy, traffic routing, and observability in one product system. Run Peakhour Edge as the full delivery layer, or keep an existing edge provider in place while WAAP, API security, bot decisions, rate limits, cache policy, image optimisation, TLS, logging, load balancing, and origin shield stay attached to one request path.
Application security controls for WAAP, API security, bot decisions, rate limits, cache policy, image optimisation, TLS, logging, load balancing, and origin shield.
Portfolio summary
Security, delivery, and platform controls use the same request decision core and retain a shared evidence trail.
WAAP, API security, bot control, and rate limits
Decide
Caching, image optimisation, and origin shield
Serve
TLS, load balancing, logs, and SIEM streams
Operate
The product portfolio is not a pile of separate tools. A cache rule, rate-limit rule, or origin-shield policy can use bot verification, geography, API path, payload policy, traffic-control state, and log evidence so teams can see why traffic was served, routed, challenged, throttled, or blocked.
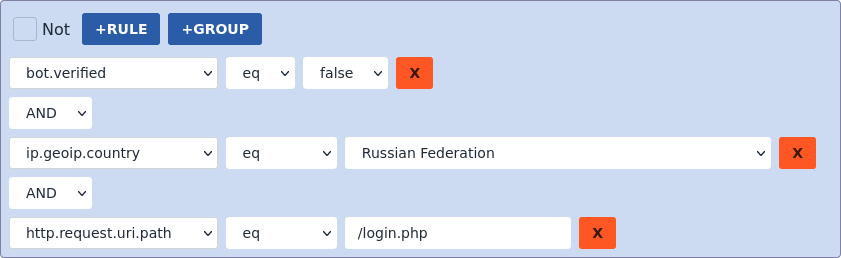
Start from a focused rule builder, then follow the linked controls into cache policy, API protection, bot control, image optimisation, and log forwarding without repeating the product grid.
01Portfolio family
Inspect requests before origin, then allow, challenge, throttle, or block with evidence attached.
WAF rules, OWASP controls, DDoS checks, and API-aware protection before origin.
REST, GraphQL, and WebSocket controls for auth context, schema drift, and endpoint abuse.
Behaviour scoring, browser checks, and challenge actions for scrapers, credential stuffing, and fake users.
Path, identity, ASN, IP, and fingerprint thresholds with block, throttle, or challenge actions.
Reputation, proxy, hosting, and geography signals used by WAAP, bot, and rate limit decisions.
Detect residential proxy traffic so fraud and scraping rules can treat it differently from normal users.
Flag exposed credentials before account takeover attempts become successful logins.
02Portfolio family
Serve more traffic from cache, protect origin capacity, tune payloads, and steer misses with request evidence attached.
Dynamic caching, cache keys, bypass logic, purge behaviour, and origin-load reduction for Peakhour Edge or an existing delivery path.
AVIF, WebP, resize, quality, and responsive variants served with cache and delivery evidence intact.
Shield cache hierarchy that collapses misses, reduces direct origin pressure, and keeps repeated cache misses away from backend capacity.
Layer 7 flood mitigation, clean path routing, and request evidence for service availability reviews.
03Portfolio family
Operate certificates, traffic steering, logs, and implementation support as part of the product system.
Certificate issuance, renewal state, TLS policy, and encrypted delivery between users, Peakhour, and origin.
Global and local load balancing with health checks, geo routing, failover, origin pool selection, and traffic-control evidence.
Decorated access logs delivered to SIEM and analytics destinations with cache, security, and request decision context.
Delivery migration, WAAP policy review, bot tuning, cache rule design, and operational handover.
Review the Peakhour system as security decisions, cache and image policy, TLS state, load balancing, origin shield, and log evidence rather than isolated products.
© PEAKHOUR.IO PTY LTD 2026 ABN 76 619 930 826 All rights reserved.